CPENT & LPT Master Review: The 5 Domains
If you are preparing for the EC-Council CPENT or LPT Master, you already know it is a grueling exam. Time management and a solid methodology are everything. Here is a spoiler-free, straight-to-the-point breakdown of the domains and key concepts you absolutely must know to survive.
Certifications Achieved
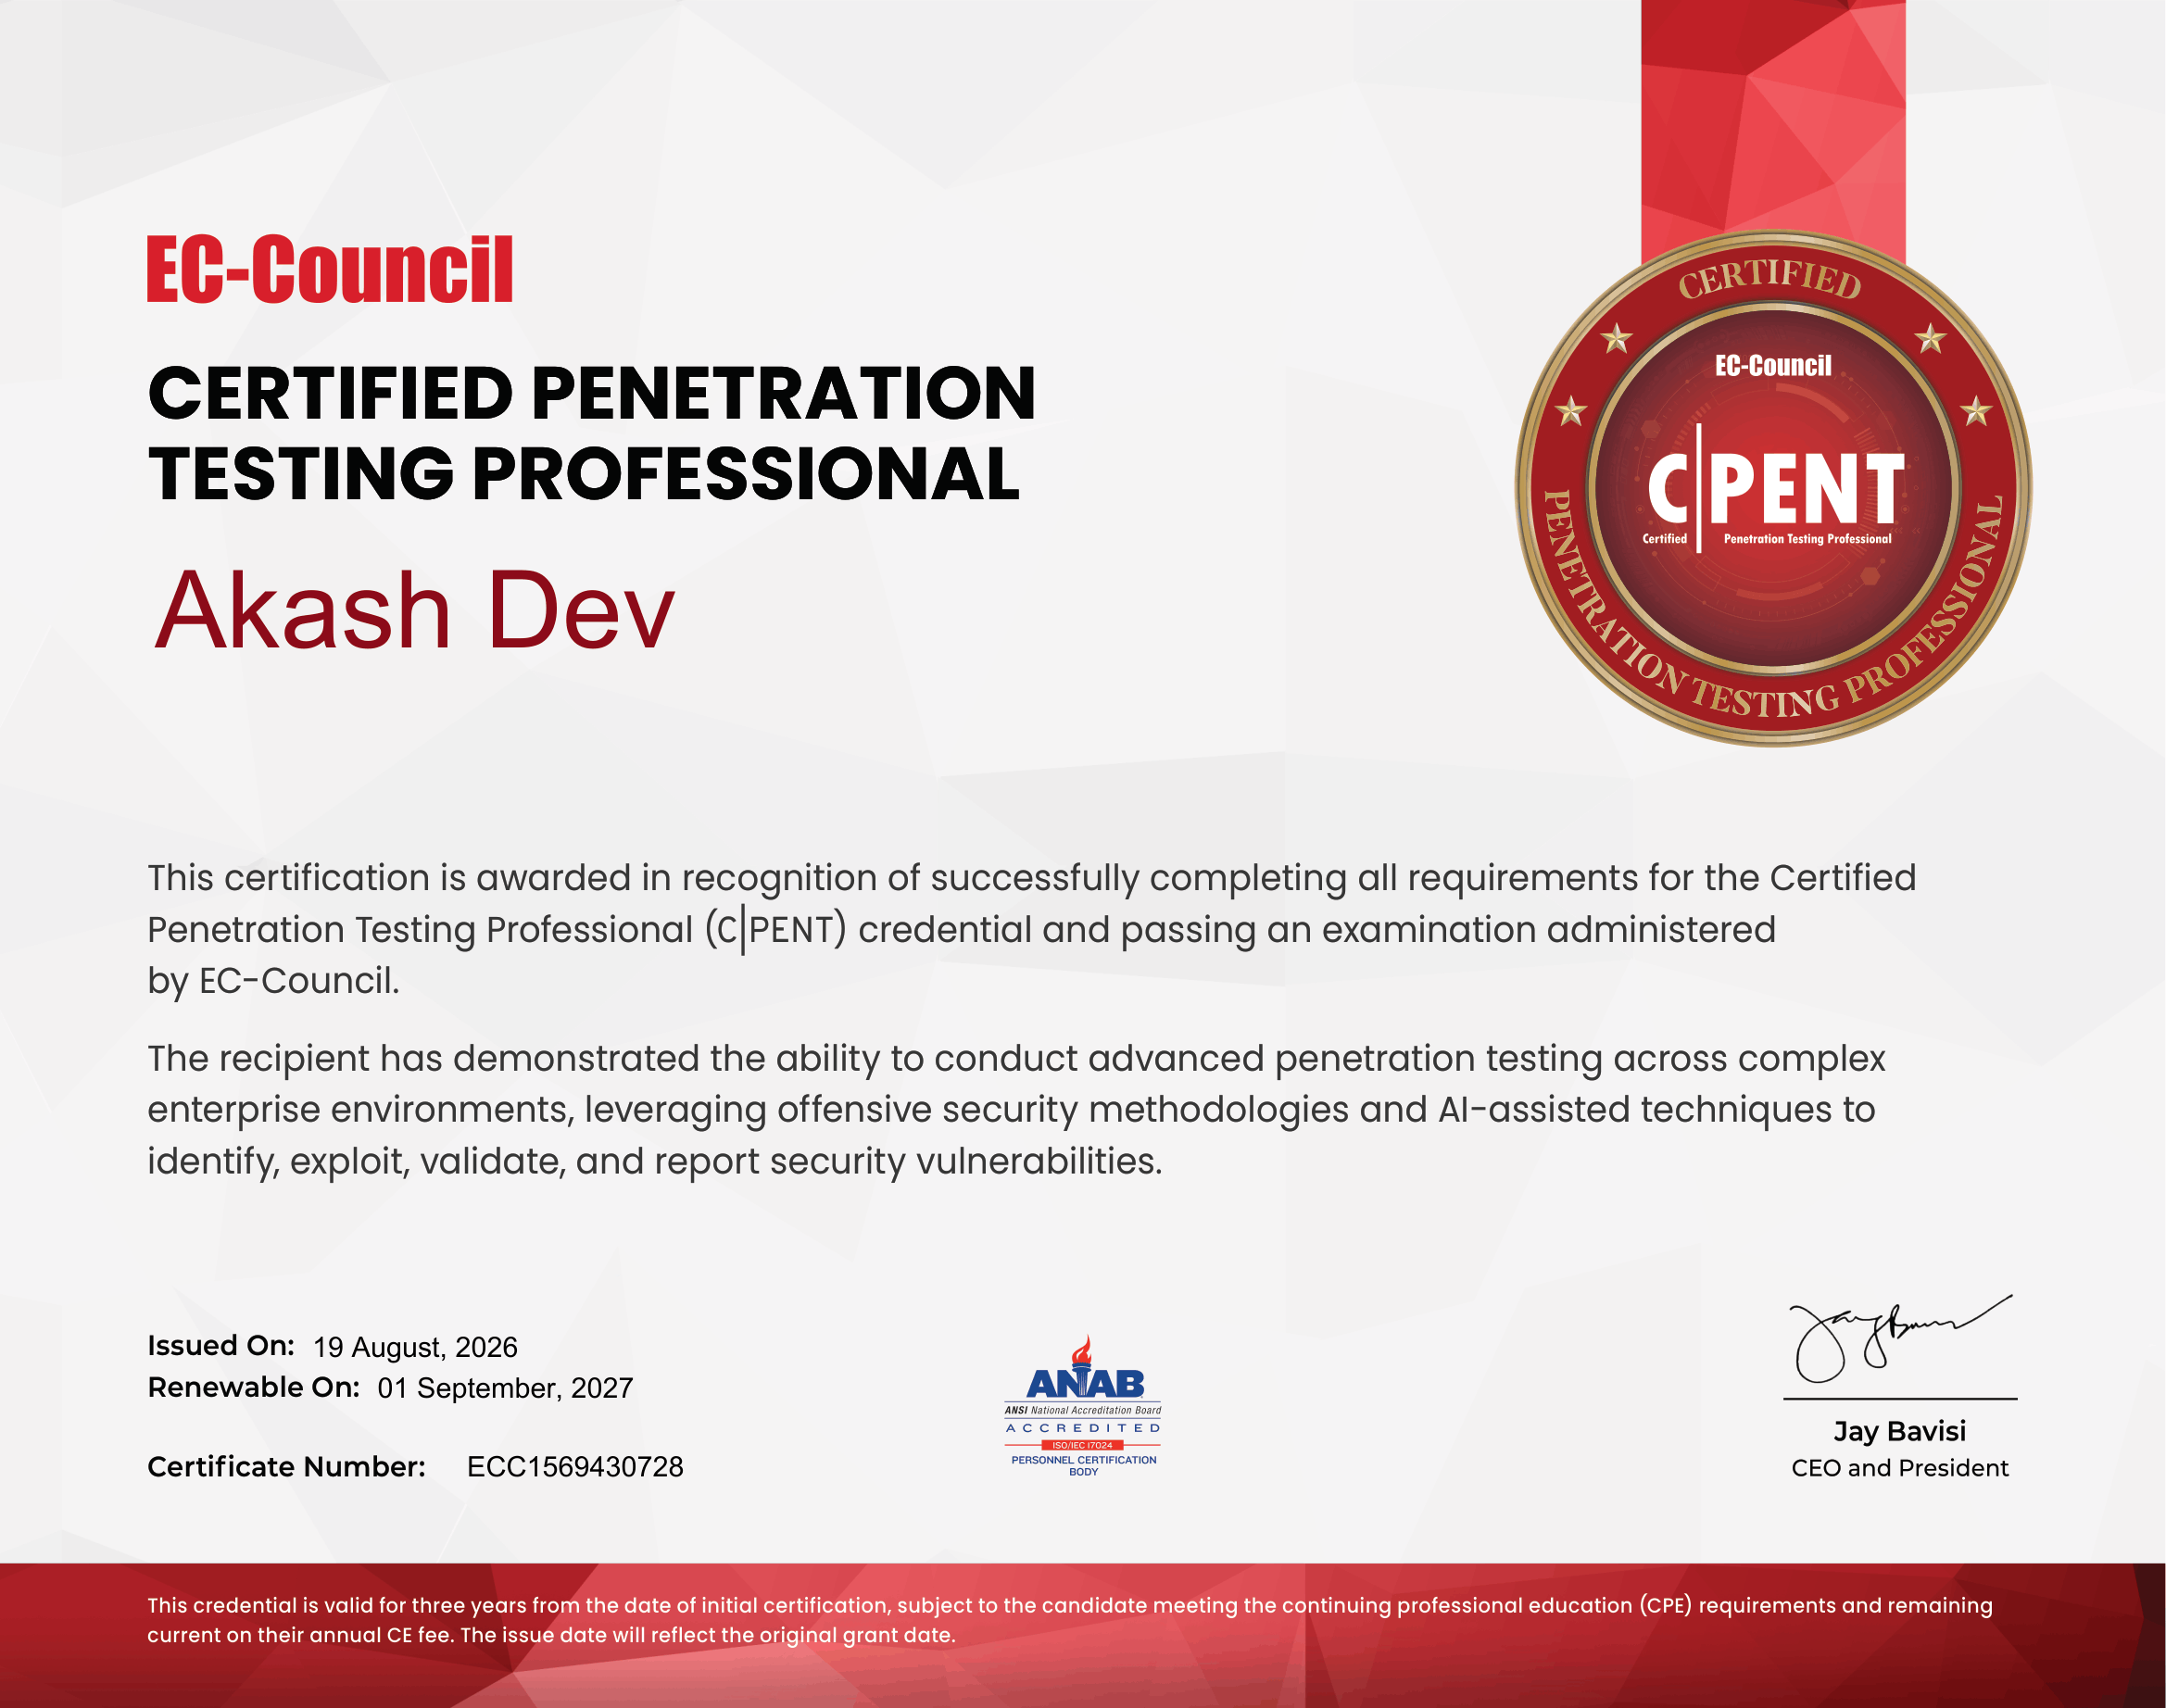
CPENT Certificate
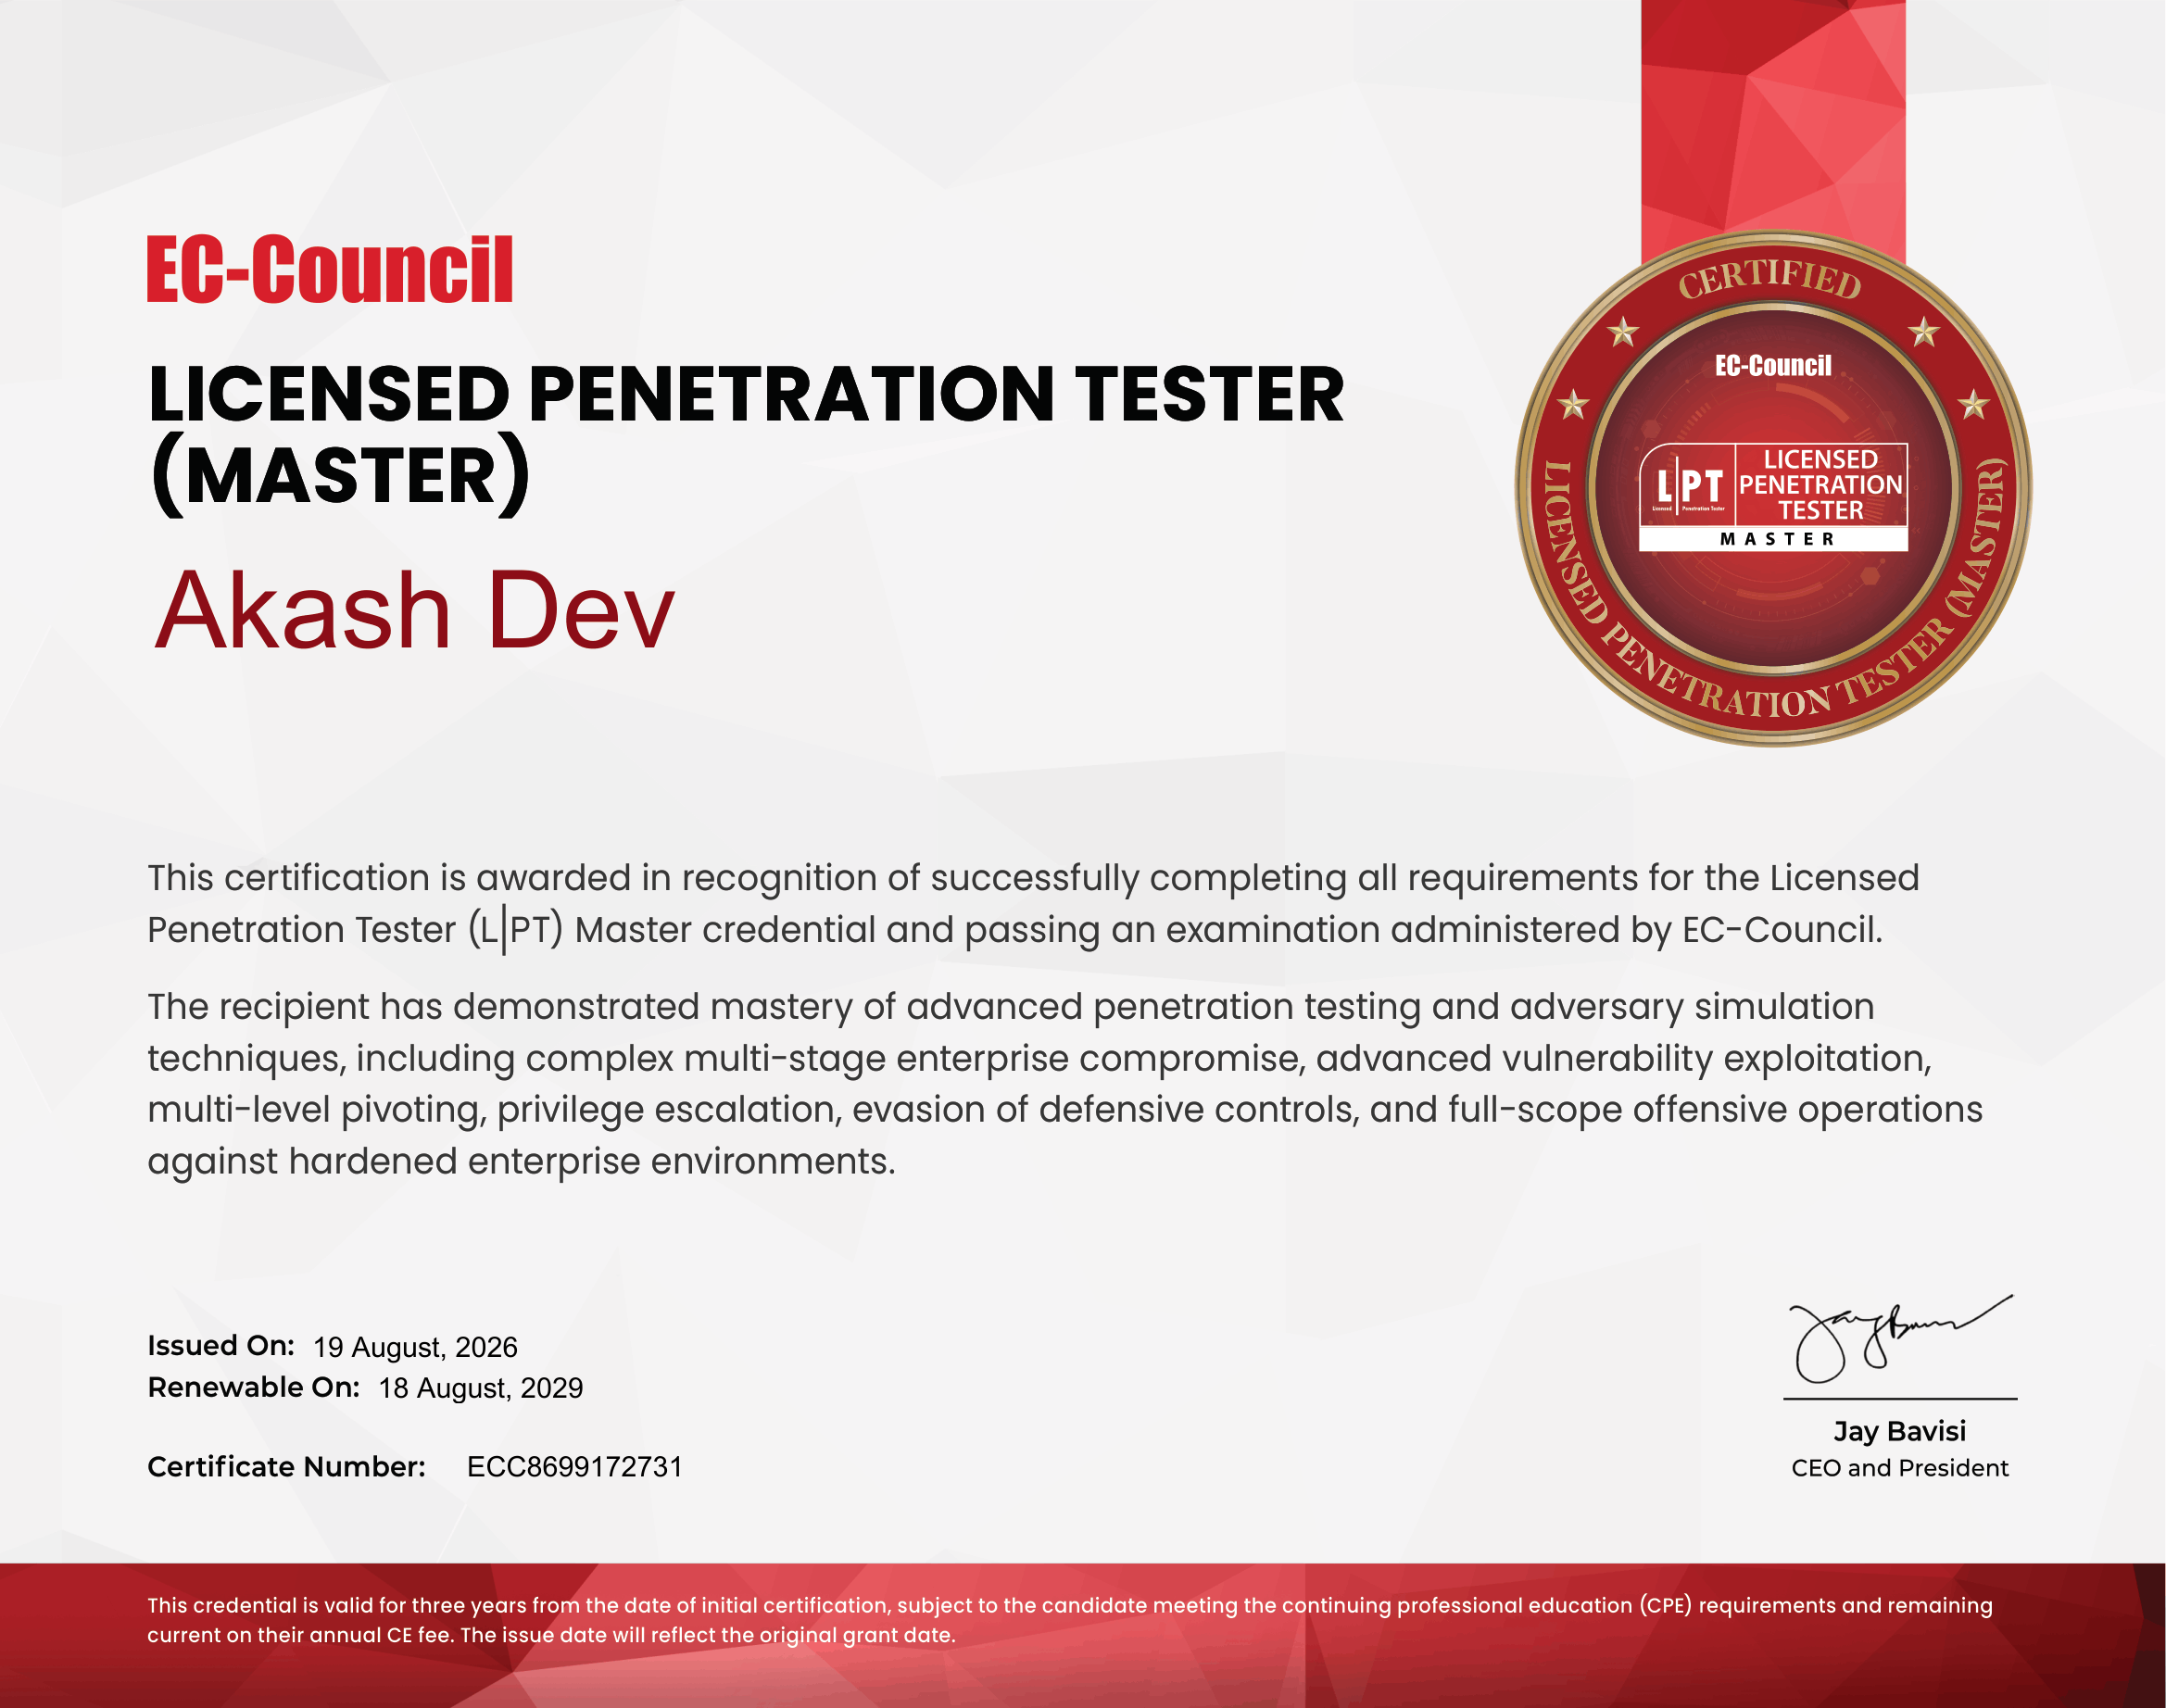
LPT Master Certificate
The Exam Ranges & Key Concepts
1. Active Directory (AD)
The Goal: Enumerate the forest, find domain controllers, and exploit trust relationships.
Key Concepts: AS-REP Roasting, SMB enumeration, and extracting Hashes.
2. Binary Analysis
The Goal: Dynamic analysis of binaries to bypass protections and escalate privileges.
Key Concepts: Analyzing registers (like $r8 or $ss) at runtime, identifying memory offsets, and cracking shadow hashes.
3. IoT (Internet of Things) Firmware
The Goal: Reverse engineer firmware to extract filesystems and find backdoors.
Key Concepts: Extracting Squashfs/JFFS2 filesystems, hunting for hardcoded credentials (using grep/strings), and analyzing compiled C scripts.
4. Web Application Exploitation
The Goal: Chain web vulnerabilities to gain a foothold on the server.
Key Concepts: Bypassing file upload restrictions (PHP reverse shells), brute-forcing OTPs, and Local File Inclusion (LFI) to Apache log poisoning.
5. CTF & Pivoting
The Goal: Lateral movement and deep network penetration.
Key Concepts: Finding hidden SSH keys (id_rsa), hijacking cron jobs for root access, exploiting SUID binaries, and SQL database enumeration.